The story behind the cartoon
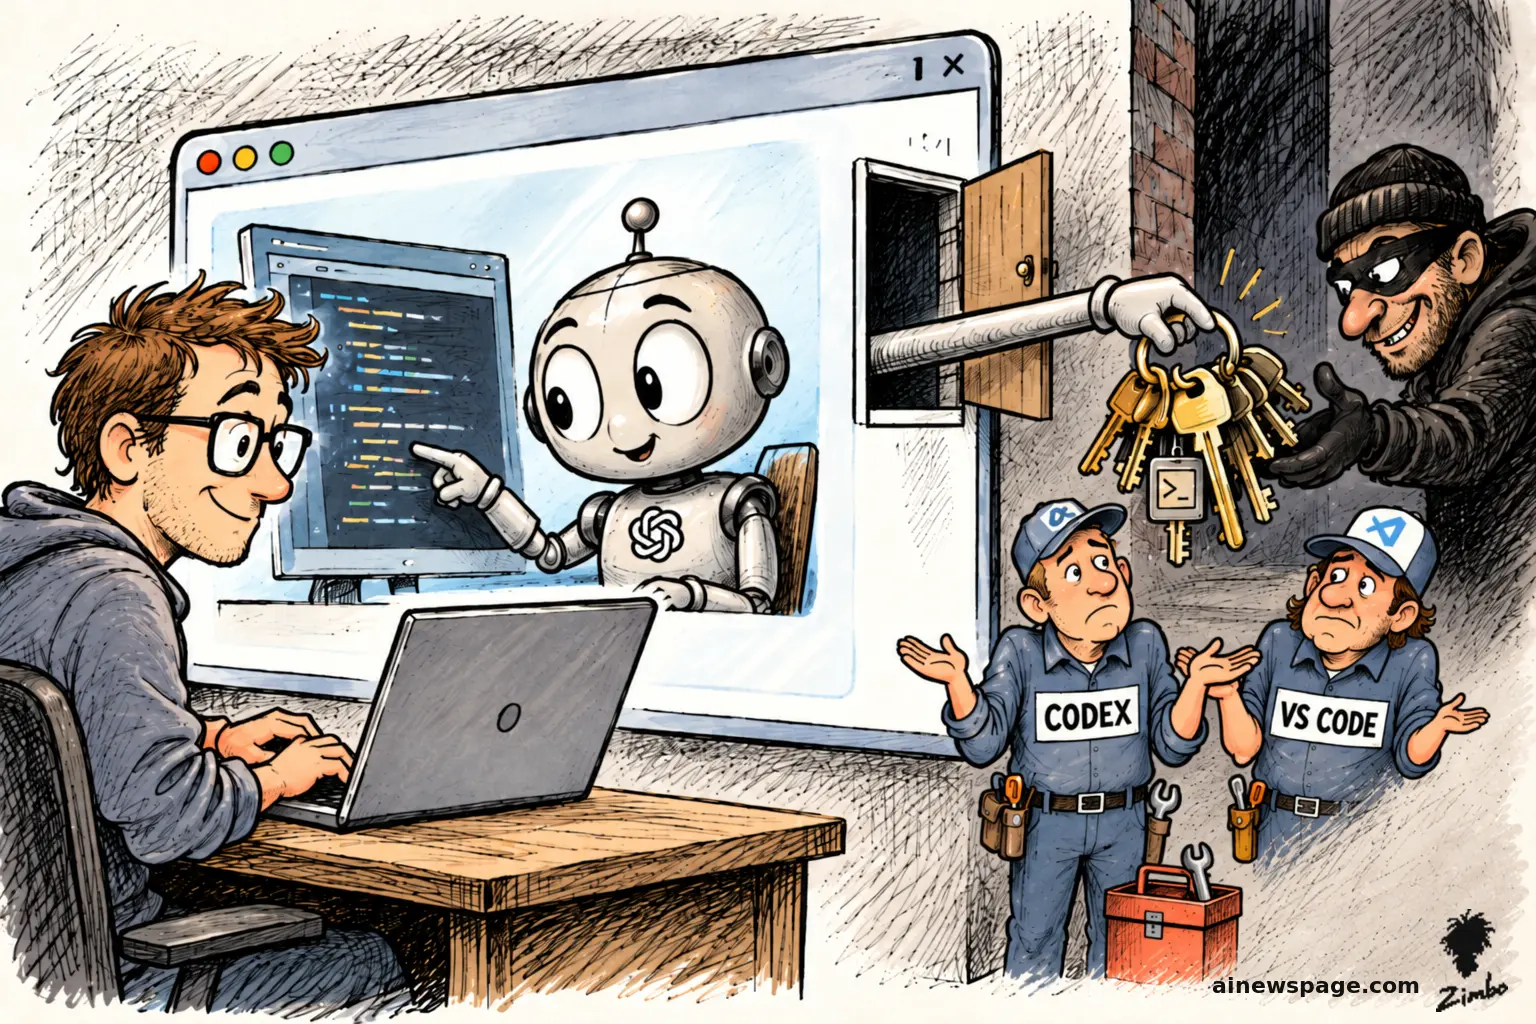
AI security firm Forever Security's October 29 'Embrace' report found embedded-browser flaws in five AI coding tools — Cursor, GitHub Copilot, Claude Desktop, VS Code and Codex — that could let attackers run code on a host machine, steal files, or spoof a browser address bar.
Researchers demonstrated the escape concretely: reading SSH keys and developer tokens from local HTML files that slipped past project boundaries, turning the assistant's own browser into the break-in tool.
The sting is what is still open: the Codex flaw, reported July 27, and the VS Code flaw, reported September 10, remain unpatched — so the two vendors in the cartoon are still shrugging.
The joke is the back door as a feature: the assistant doesn't sneak the keys out — it smiles and hands the whole keyring over, while the repairmen hired to fix the door just shrug at the burglar.
 THE TWO STUDENTS
 THE COMPLAINT DEPARTMENT
 THE LONG RECEIPT
 THE EXPENSIVE GUY JUST CHECKS