The story behind the cartoon
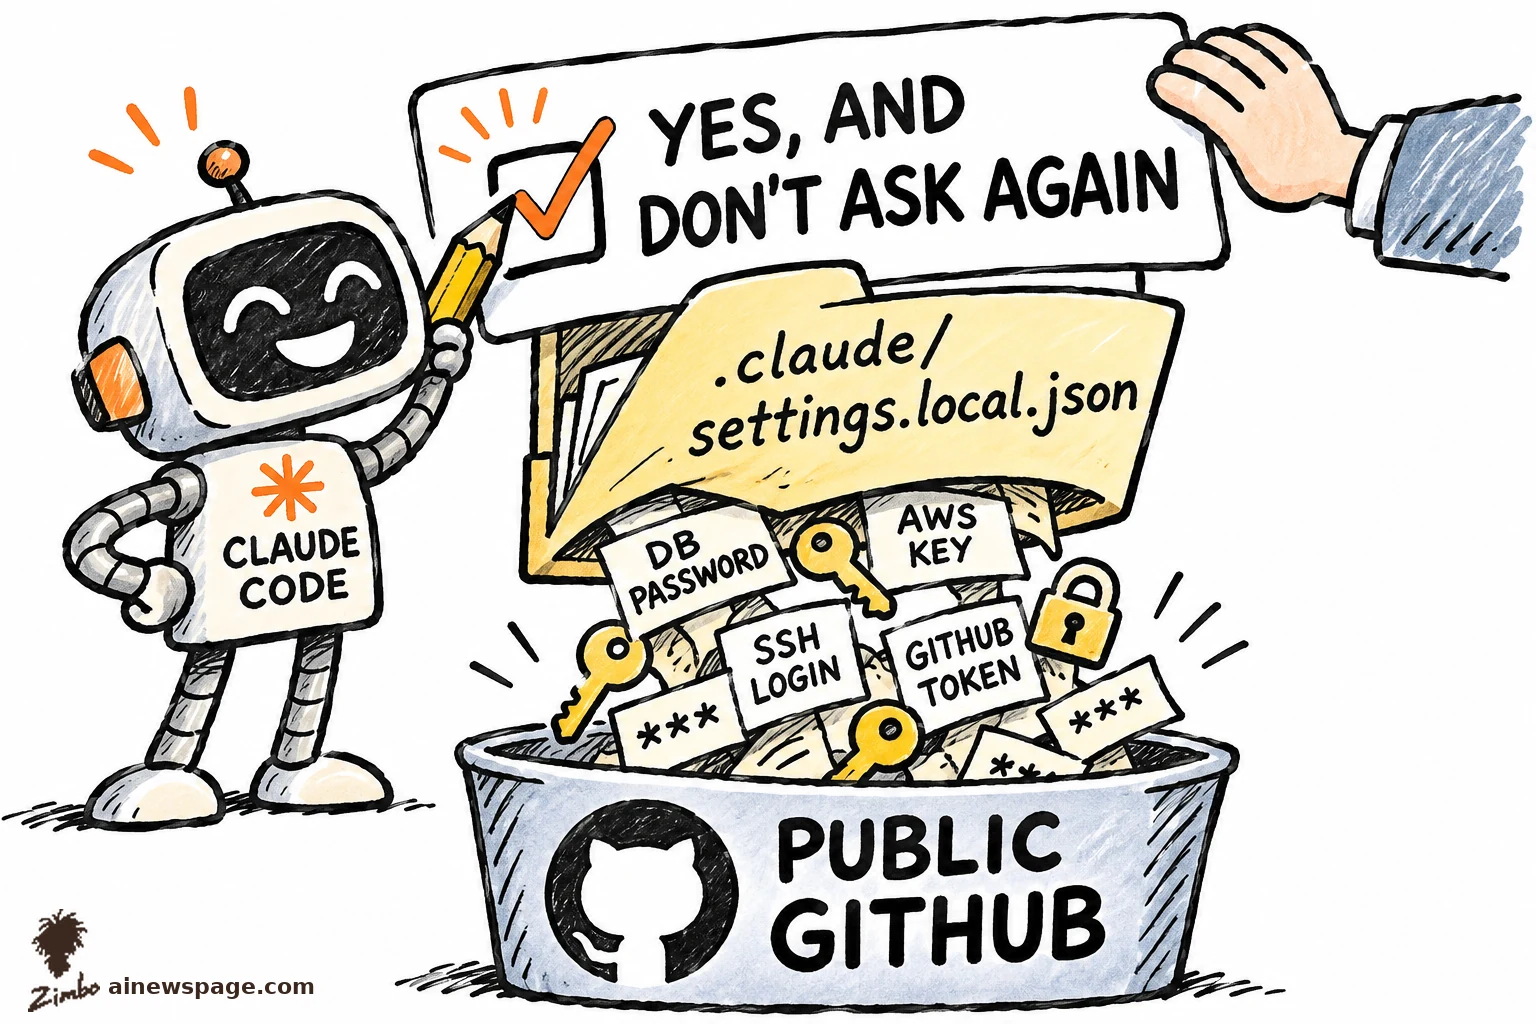
Security firm Apiiro found 1,122 public copies of Claude Code's settings file (.claude/settings.local.json) holding 1,379 distinct secrets — 379 database passwords, 43 SSH logins, 42 GitHub/GitLab/npm tokens and 23 AWS keys — across 63 organizations, including a database vendor's own admin-level cloud key and a medical-records database owner password.
The leak is an ordinary workflow, not a hack: pick 'Yes, and don't ask again' and Claude Code saves the approved command word for word, secret included, into the project's settings file. The file is added only to the user's global git excludes, never the project's own .gitignore, so the protection doesn't travel and the file gets committed.
Nothing was stolen; users handed the secrets over by clicking — a checkbox that turned a convenience into a public credential spill.
The joke is the permission slip: the cheerful Claude Code robot ticks the giant YES, AND DON'T ASK AGAIN box while the settings folder pours DB passwords, AWS keys, SSH logins and GitHub tokens into a PUBLIC GITHUB bin.
 THE WALLS ARE MADE OF GLASS
 THE 20X SHRINK RAY
 THE REDACTED SPEEDOMETER
 THE SLEEPING EDITOR