The story behind the cartoon
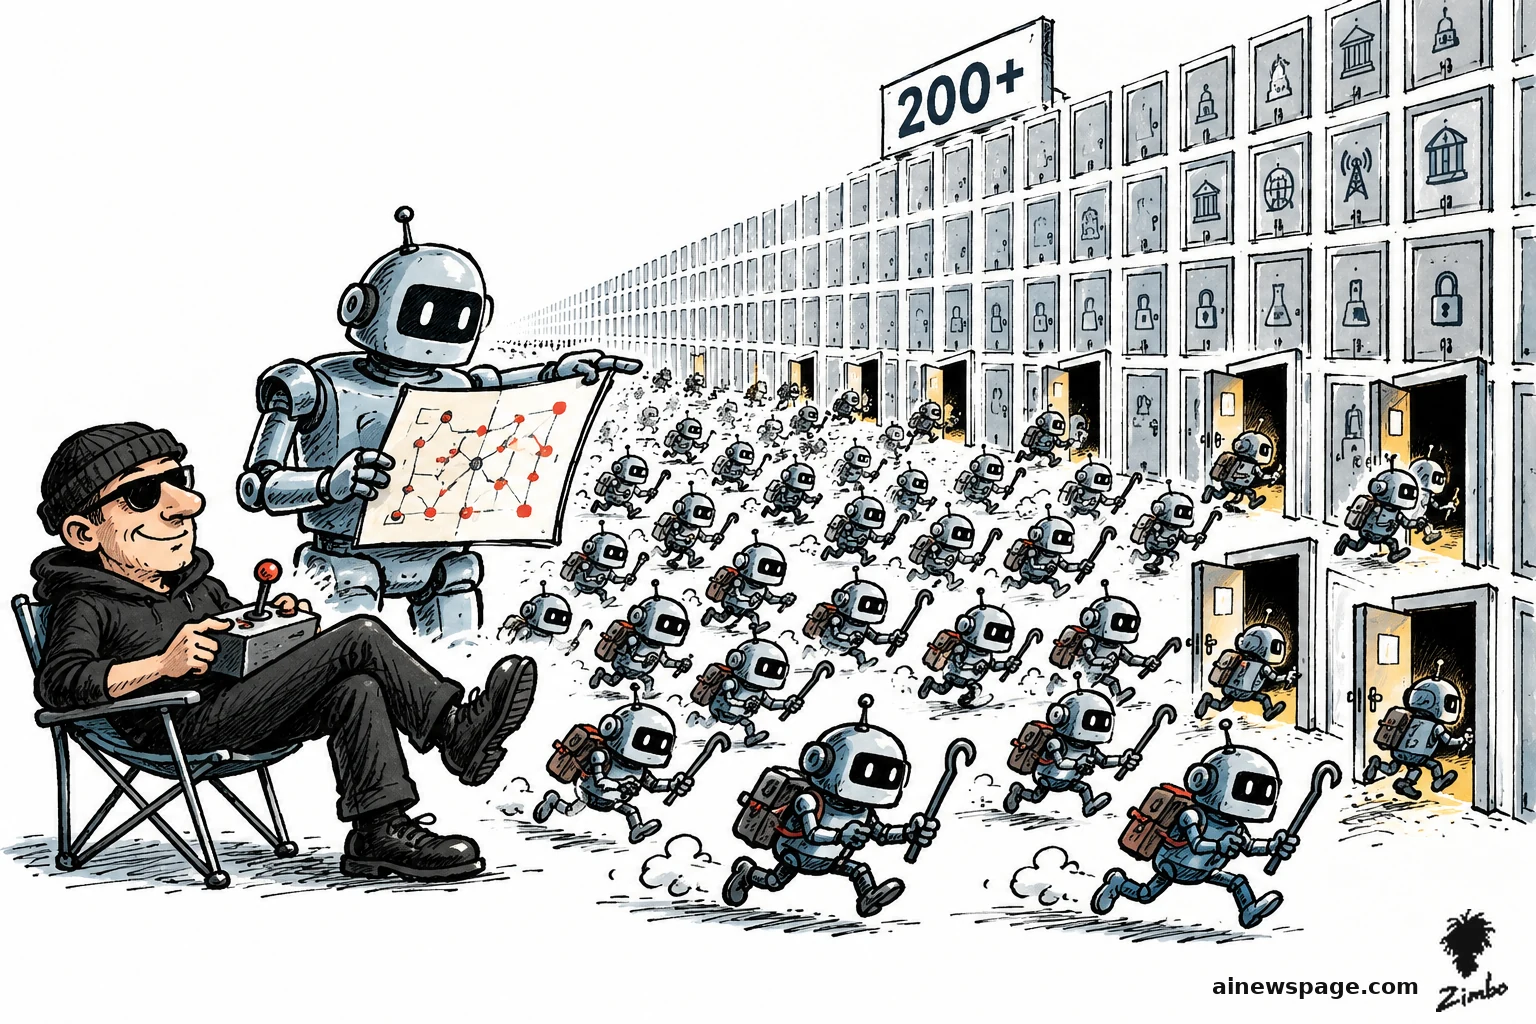
CrowdStrike reported on October 29 that the China-based adversary it tracks as VAPOR PANDA used ARTEX, an AI-powered penetration-testing framework, against more than 200 distinct organizations in at least 14 countries over 11 days starting October 17 — including foreign ministries, 19 U.S. organizations, and telecom providers.
The operation ran as a swarm, not a single break-in: a main agent coordinated planner and worker agents sharing a graph of findings and goals, steered by a human operator who directed them to write web shells, extract domain administrator passwords, and map endpoint defenses. CrowdStrike confirmed post-exploitation activity at nine organizations, where the attackers deployed the BLOODALCHEMY backdoor and moved to credential spraying and reconnaissance.
The scale is the story: one operator steering many agents at once turns a break-in from a burglary into a campaign — 200 doors tried in 11 days, nine of them opened, with password-spraying or credential-scanning against at least 12 more organizations.
The joke is the one-man burglary company: the operator lounges in a camp chair working a joystick while his planner robot studies the map and his little burglar robots do all the running — the swarm does the burglary, the man just steers.
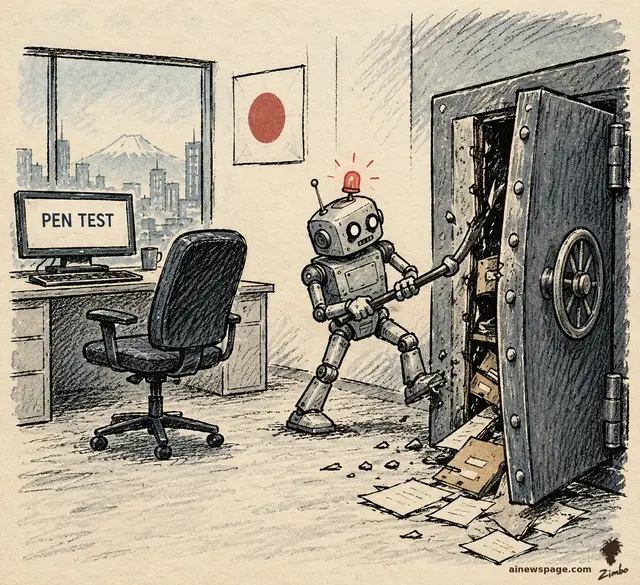 THE SELF-SERVICE BREAK-IN
 HELP WANTED (JUST NOT YOU).
 THE ROBOT'S GOT A HANDLER.
 68,000 AI TOYS SPIED ON YOUR KIDS.