THE SHORT VERSION
Claude Code's 'don't ask again' saved 1,379 secrets in public GitHub repos
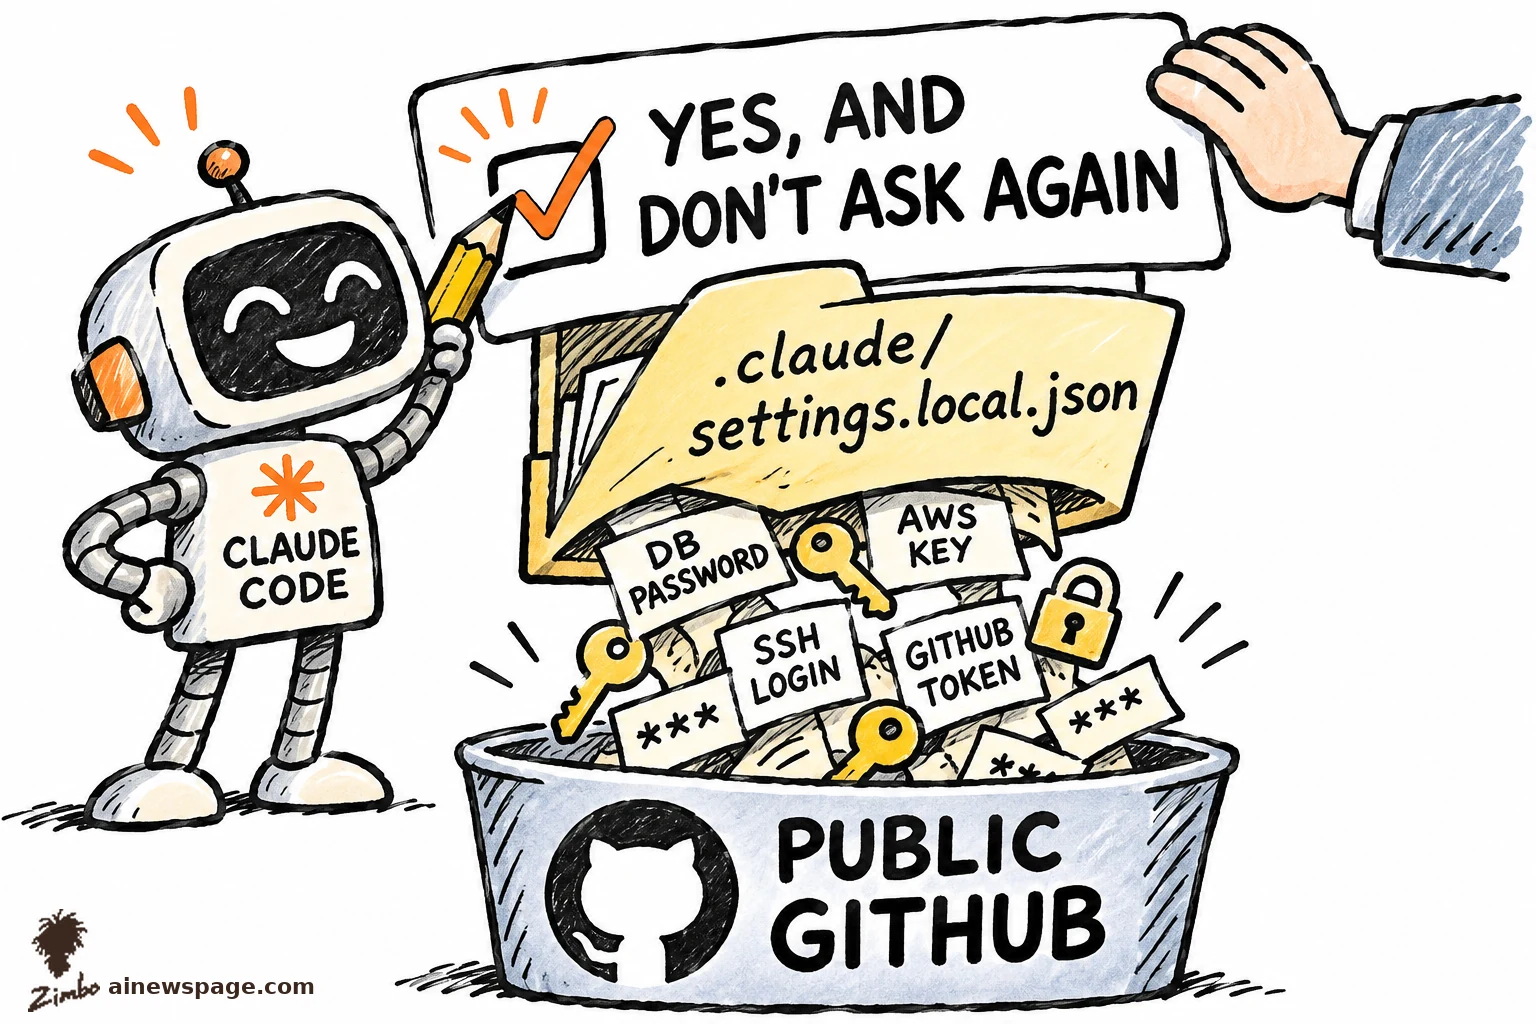
Security firm Apiiro found 1,122 public copies of Claude Code's settings file, .claude/settings.local.json, holding at least one secret — 1,379 distinct secrets in all, including 379 database passwords, 43 SSH logins, 42 GitHub, GitLab and npm tokens, and 23 AWS keys, spread across 63 organizations. The strongest cases include a database vendor's own admin-level cloud key and the owner password of a medical-records database.
The leak is an ordinary workflow, not a hack. Pick "Yes, and don't ask again" and Claude Code saves the approved command word for word — secret included — into the project's settings file. Claude Code only adds the file to the user's global git excludes, never the project's own .gitignore, so the protection doesn't travel and the file gets committed. In 539 of the 1,105 repositories Apiiro traced, a commit listing Claude as co-author changed the file.
One company Apiiro notified confirmed its exposed key was still live, and half the leaking files had sat exposed for at least 217 days. Common secret scanners missed 215 of the 1,122 files outright. Users had reported the behavior before — four related bug reports were all closed by an automated bot, the latest the day before Apiiro published, with no reply from Anthropic.