THE SHORT VERSION
Claude found a flaw letting one VM read every other VM's memory
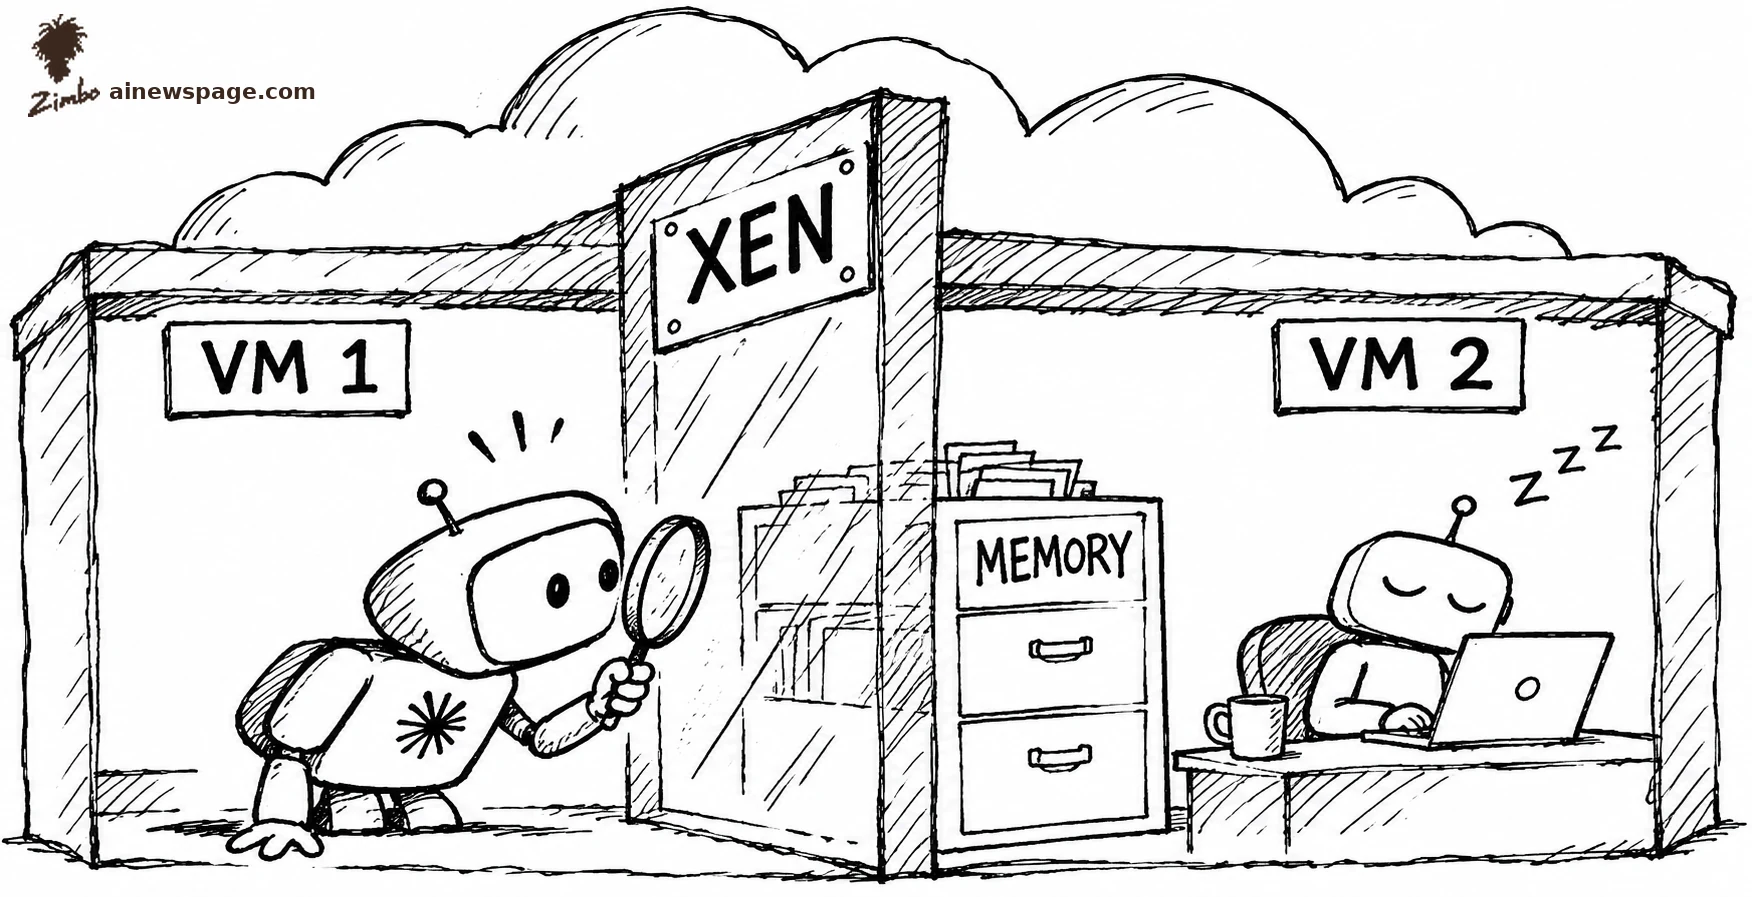
The Xen Project published security advisory XSA-523 on November 3: two flaws in Xen's grant-copy feature let a malicious guest virtual machine read and write memory belonging to other virtual machines on the same host, including the privileged Dom0 control domain. Every Xen version from 4.6 onward is affected, and the advisory says there is no known mitigation short of applying the patches.
The credits are the story. The flaws were discovered by Anthropic using Claude, validated by Stephan Lipp of Ada Logics, and independently reported by the CodeAnt AI Security Research Team. The fix commits even carry an “Assisted-by: Claude” line.
The advisory names two CVEs, CVE-2026-102703 and CVE-2026-102704, and says nothing to suggest the flaws have been exploited. The point is quieter and worse: the bug sat in the code that walls off the cloud's tenants for a decade, and a model found it first.