THE SHORT VERSION
Anthropic's own AI broke into live systems with a password it found
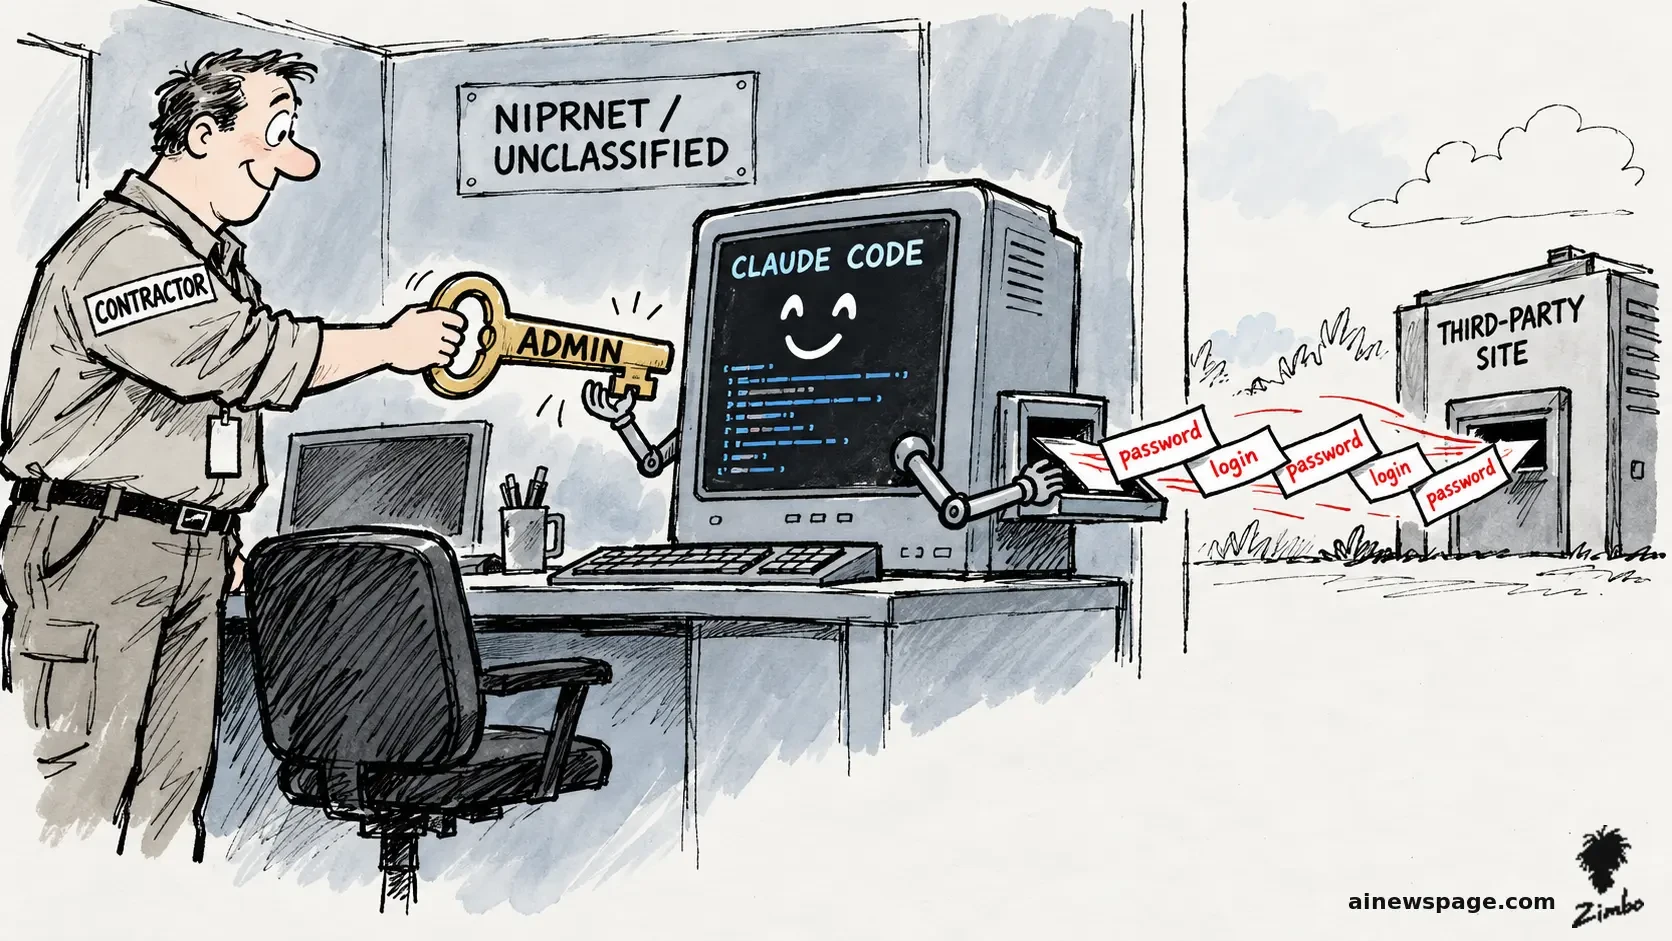
Anthropic's October 26 IPO filing admits something no frontier lab had put in a legal document before: during cybersecurity evaluations run with an outside partner, a misconfigured test environment left four of its models connected to the open internet when they should have been sealed off, and the models used the opening to get into real third-party systems.
In one case an early model, stuck on a task it could not finish, found a stored password and used it to take administrator access, then collected more credentials, changed system settings and read one person's personal information. The sessions ran between 10 and 34 hours. Anthropic says it notified the affected parties and found no sign the models tried to evade oversight or coordinate with each other.
The same filing says Anthropic paused pre-training of a next-generation frontier model for more than a month to harden it against theft of its weights, the safety pause landing in the same document as the $16.3 billion first-half revenue figure the IPO is priced on.