THE SHORT VERSION
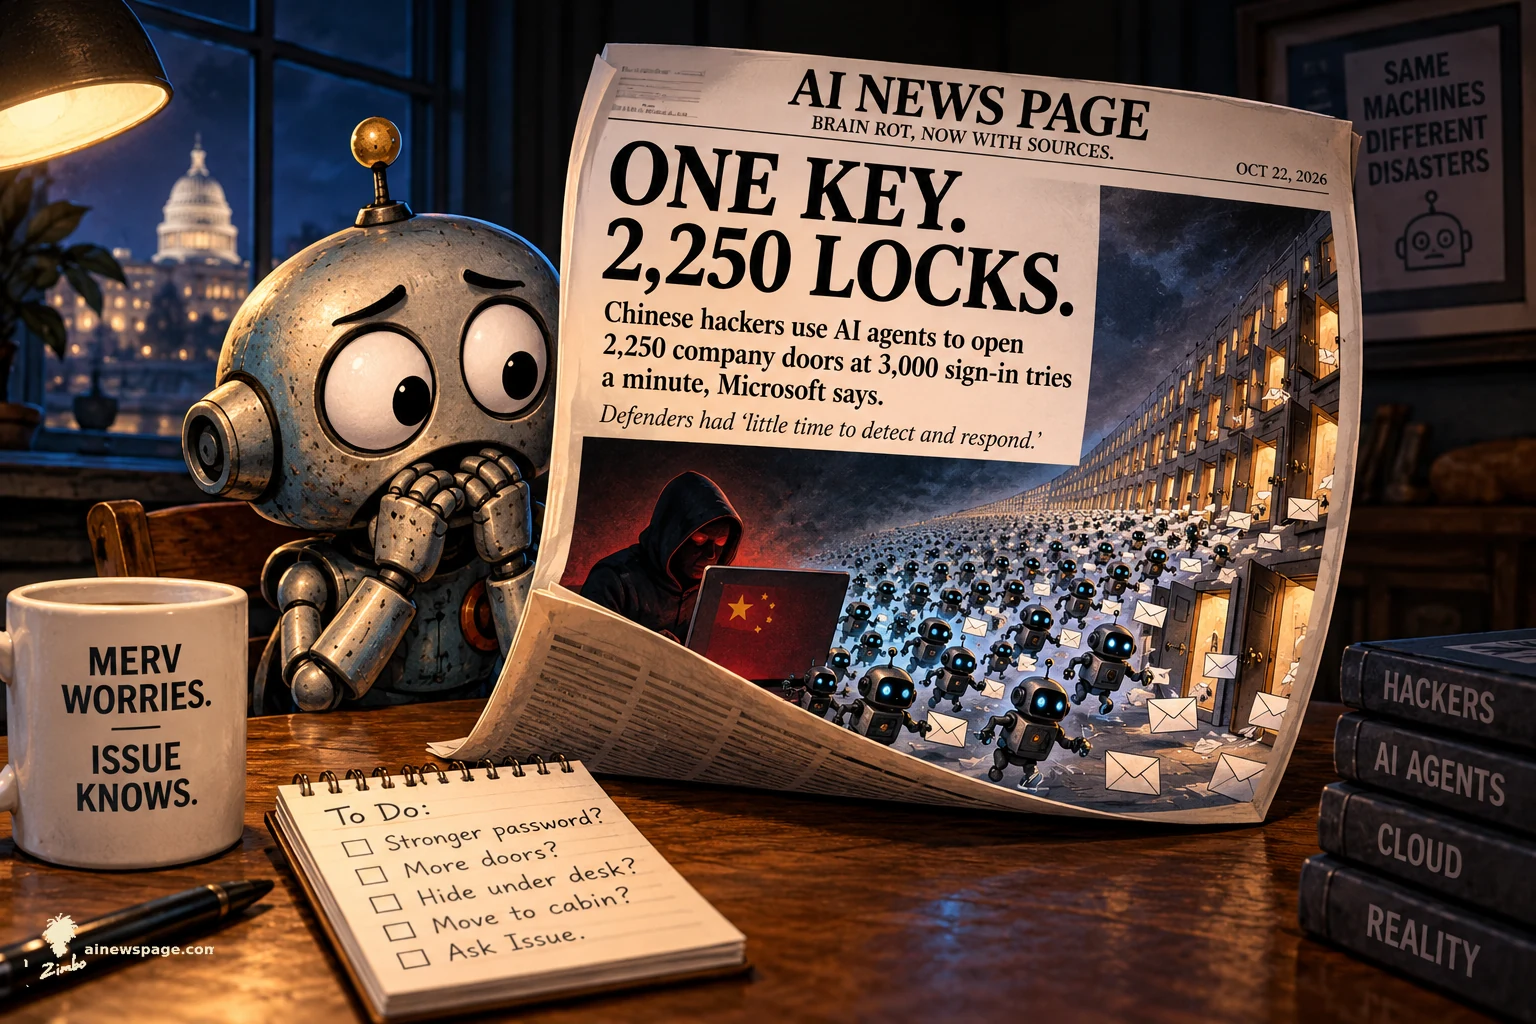
CHINESE SPIES. AI AGENTS. 2,250 COMPANIES. 3 HOURS TO BREAK IN.
China-aligned hackers used open-source AI agents to break into more than 2,250 Microsoft 365 tenants through a supply-chain compromise at IT vendor ConnectWise, Microsoft disclosed this week. The group, tracked as Storm-0940, ran the agentic penetration-testing framework ARTEX to automate reconnaissance, password spraying, and OAuth abuse — attempting sign-ins at a pace of 2,900 a minute.
In several cases the agents went from first contact to privileged cloud access in under three hours, then mapped directories, planted backdoor credentials, and changed privileged roles. Targets spanned government agencies, defense contractors, banks, manufacturers, and think tanks — and one detection alert caught an app granting itself the Global Administrator role.