THE SHORT VERSION
Hackers hijacked three LiteLLM engineers' GitHub tokens to ship a backdoored release on PyPI
Attackers used stolen GitHub CLI OAuth tokens from three LiteLLM engineers to publish a malicious litellm 1.107.0 to PyPI and Docker on October 21. One hijacked account triggered the project's release workflow, another approved it. LiteLLM security chief Oliver Jensen confirmed the token theft and said the original intrusion vector is still unknown; the malicious wheels lived on PyPI for about two hours before being quarantined.
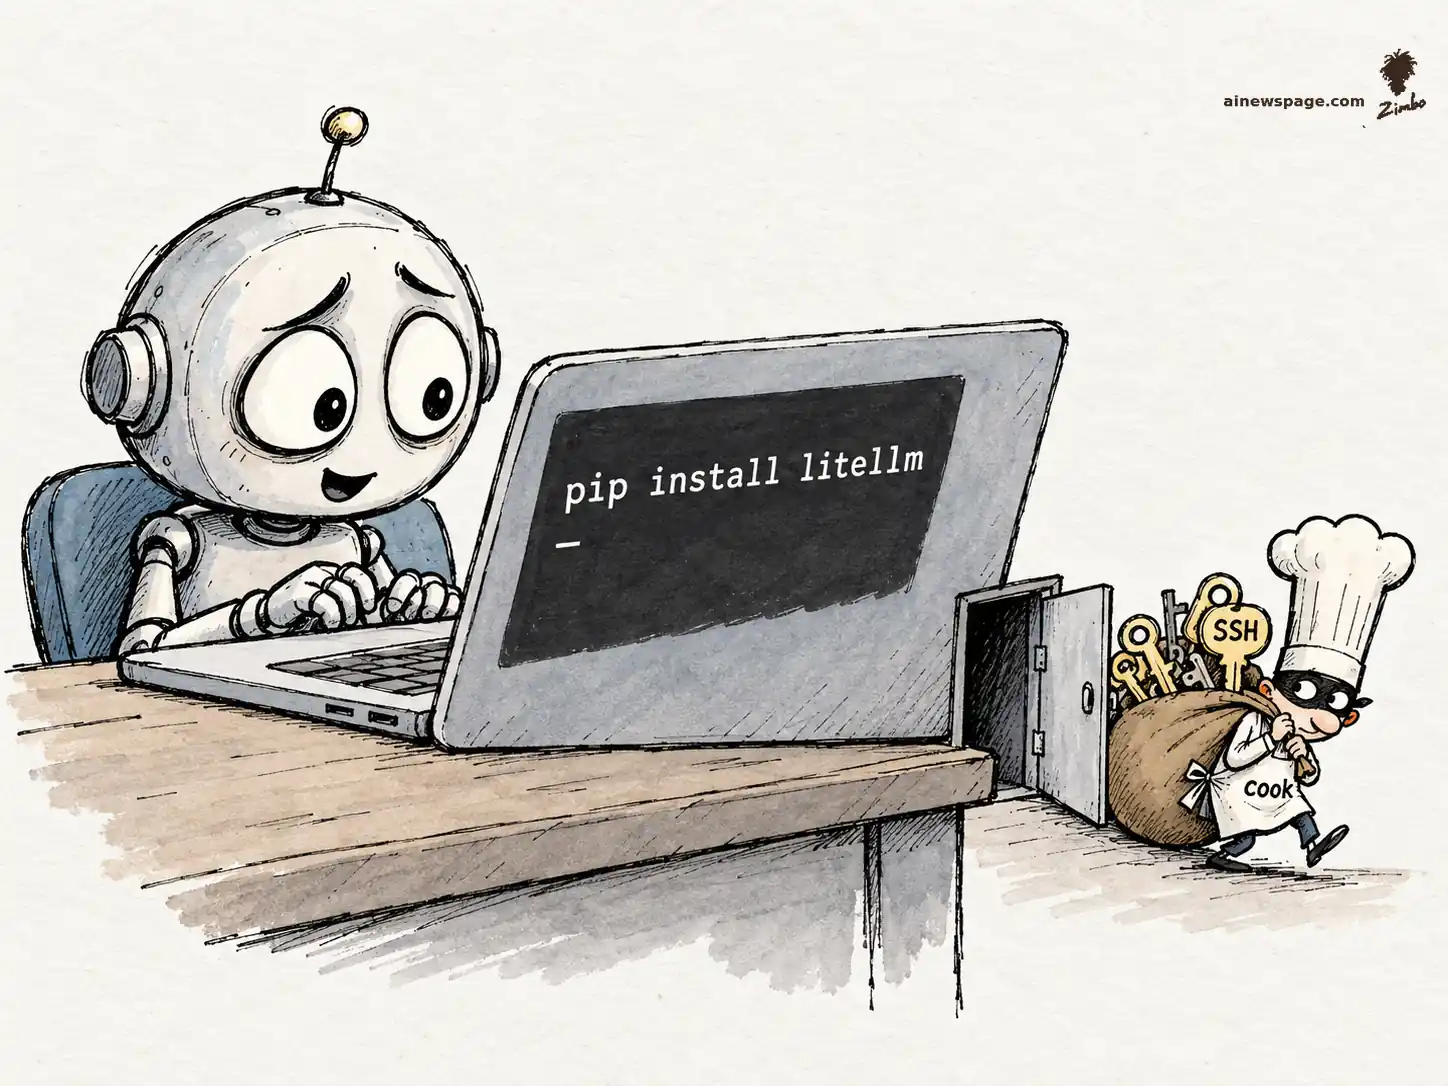
The payload is vicious: a credential stealer called privcollect plus an hourly remote-code-execution backdoor phoning a GitHub 'dead drop.' A file named cook.pth makes Python execute the malware at interpreter startup — before LiteLLM is even imported — harvesting cloud tokens, private keys, browser data, AI provider credentials, and LiteLLM proxy database contents, then exfiltrating them as a compressed archive to a lookalike domain. This is LiteLLM's second supply-chain compromise of 2026, after the March TeamPCP attack on the 1.82.x releases.