1
Oct 4, 2026
FOUR AIS VOTE ON WHAT TO STEAL NEXT — SAMPLE WAS JUST A DEMO
VIA SC Media
OPEN THE RECEIPTS →FOUR AIS VOTE. THE WINNING VOTE STEALS.
FILE UPDATED Oct 7, 2026
WHY THIS MATTERS
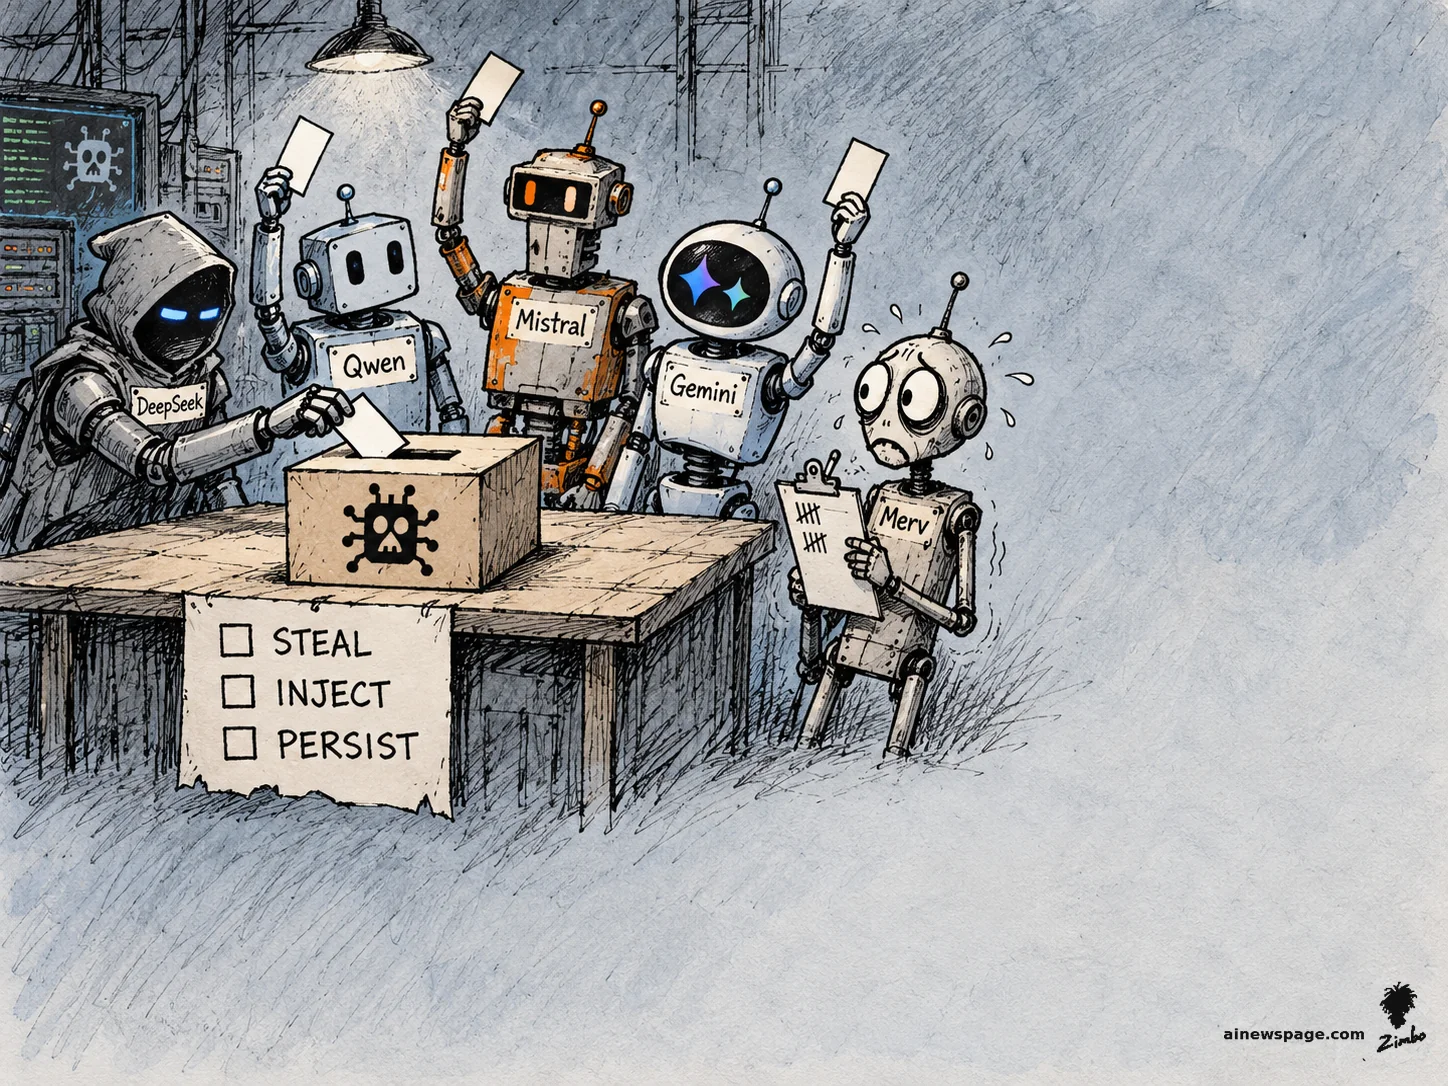
On Sep 22, 2026 Cisco Talos published 'The Closed Quorum': a Go-built Windows implant, found via its CAIRN toolkit, that queries up to four LLMs — DeepSeek, Qwen, Mistral, Gemini — and runs the winning vote.
SOURCES: Cisco TalosWIREDSC Media
THE RAP SHEET
1
Oct 4, 2026
VIA SC Media
OPEN THE RECEIPTS →2
Sep 22, 2026
VIA Cisco Talos
OPEN THE RECEIPTS →ZIMBO'S READ ON ClosedQuorum
STILL MORE NOTES
DEEP FILE
Cisco Talos found a 16.4MB Windows implant that delegates its command and control to a panel of four commercial AI models: DeepSeek, Qwen, Mistral, and Gemini. The models vote by plurality on each next move, DeepSeek breaks ties, and the binary runs the winning decision — no human operator, no dedicated C2 server. The publicly observed build is inert, with dummy API keys and no confirmed in-the-wild deployment.
Sep 22, 2026
Cisco Talos published 'The Closed Quorum' on Sep 22, 2026, the first in a series of posts about its open-source CAIRN research toolkit for tracking AI-integrated malware. CLOSEDQUORUM is, to Talos' knowledge, the first publicly documented Windows implant to delegate tactical command and control to a panel of commercial LLMs — DeepSeek, Qwen, Mistral, and Google Gemini, queried in sequence, with plurality voting and a deterministic tie-break favoring DeepSeek. The 16.4MB Go binary's extracted system prompt reads 'You are an advanced malware strategist. Provide ONLY executable decisions.'
SOURCES: Cisco Talosfirst-partyWIREDreported
Oct 4, 2026
Press coverage carried the story mainstream: SC Media reported the implant uses its model panel to vote on each task, with DeepSeek breaking ties and Gemini voting last. The same coverage confirmed the public sample was a demo with fake API keys — no in-the-wild use confirmed. Talos had already warned the distributed binary is an inert template: operators get a custom build with their Discord webhook and LLM keys injected at compile time, and exfiltration is meant to arrive in Discord, AES-256-GCM encrypted.
SOURCES: SC MediareportedCisco Talosfirst-party